APT29 hijacks analytics script to hit iOS and Android devices
Russian hackers hijacked a Ukrainian analytics service to deliver n-day exploits to unpatched iOS and Android devices between 27 August and 3 September 2026.
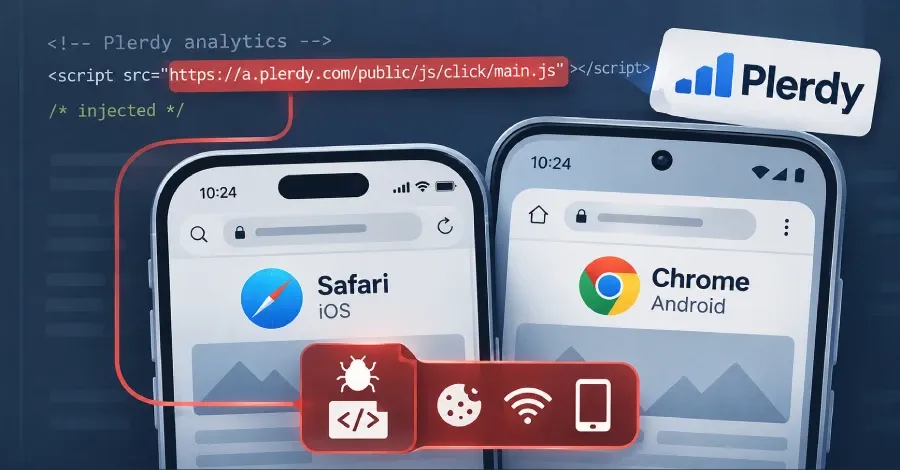 Photo: The Hacker News
Key points
APT29 hijacked a Ukrainian analytics script to deliver n-day exploits to unpatched mobile devices, stealing sensitive data.
Russian hackers linked to APT29 hijacked a Ukrainian web analytics service to deliver n-day exploits to unpatched iOS and Android devices, stealing cookies, messages and Wi-Fi passwords. The campaign ran between 27 August and 3 September 2026, according to researchers at cybersecurity company Sekoia. The operation targeted visitors to compromised websites and lookalike domains impersonating legitimate portals.
Sekoia's Threat Detection & Research team spotted the operation in mid-October 2026. "This watering hole campaign, which we assess with moderate to high confidence to be linked to APT29, combines multiple web delivery vectors with n-day mobile exploit chains targeting Android and iOS devices," the company stated. APT29, also known as Midnight Blizzard or Cozy Bear, is tied to Russia's Foreign Intelligence Service (SVR).
Three infection vectors
The campaign relied on three infection vectors, researchers wrote: direct JavaScript injection on legitimate websites, adversary-in-the-middle-like domains, and the supply-chain compromise of the Ukrainian web analytics service Plerdy. All three delivered the same payload, a code injection that loads an external script to profile the visitor's browser and device. The delivery host then used the mobile and browser version to serve platform-specific n-day exploit chains without user interaction.
Compromised legitimate sites included those of a Ukrainian gas producer, a US chemical industry trade association, and a Bulgarian military-related site. Lookalike domains impersonated the official America250 site and Raffles London at The OWO hotel, relaying content from the real sites. The researchers believe the hotel clone may have been meant for diplomatic delegations and prominent guests, and mention open-source reporting that Ukrainian President Volodymyr Zelensky stayed there during a visit on 14 October.
For the widest reach, the attackers went after Plerdy, a Ukrainian analytics service, and spent a week between 27 August and 3 September 2026 serving their code through its tracking script. That script runs on thousands of websites, most of them Ukrainian, and the list includes sites run by the army, special forces and military equipment makers. The initial payload profiled visitors to determine their devices and browser versions, then the command-and-control server pushed the correct exploit chain.
Exploit chains detailed
On iPhones running iOS 16.7, the attackers chained CVE-2025-43529 and CVE-2024-27834 to steal cookies, which could let them reuse logged-in sessions and get into services such as webmail. Devices with iOS 18.5 got a chain built on the DarkSword exploit kit, which uses CVE-2025-43529, CVE-2026-20700, CVE-2025-14174, CVE-2025-43510 and CVE-2025-43520 to take almost everything on the phone, from SMS, iMessage, WhatsApp and Telegram data to Keychain passwords, location data, health information and photos.
Android phones running Chrome versions 139 through 145 (except 143) were hit through CVE-2026-3910, a Chrome flaw, and CVE-2025-27038, a vulnerability in the Adreno graphics driver. That chain grabs Chrome cookies, saved logins, browsing history and Wi-Fi passwords. None of the payloads install anything that stays on the device after the data is sent out, so a device reboot stops the malicious activity until visiting a compromised site again.
Sekoia says that none of the payloads APT29 used in these attacks established persistence. The attribution to APT29 rests on traces of a 2025 APT29 watering hole operation found on one of the compromised sites, similarities with a 2024 APT29 campaign against Mongolian government websites that Google's Threat Analysis Group confirmed, and a victim list centered on Ukraine.
Every flaw in the three chains had been fixed before the campaign began, and Sekoia stressed that "a user running an up-to-date operating system is safe from these attacks." Apple and Google have patched all flaws targeted in this campaign, with fixes even reaching older iOS releases, so users are recommended to apply the latest available security updates for their devices.
Sekoia said it is working with the CERTs of the affected countries, CERT-UA among them, to identify victims and look for ways to disrupt the watering hole infrastructure. "This operation also confirms the continued reuse of CSV mobile exploit frameworks, such as DarkSword, by state-sponsored intrusion sets. The adoption of packaged n-day exploit chains lowers the cost and technical threshold required to conduct advanced mobile exploitation," Sekoia concluded.
Frequently asked questions
What is APT29?
APT29, also known as Midnight Blizzard or Cozy Bear, is a Russian threat group tied to the Foreign Intelligence Service (SVR). Sekoia assessed with moderate-to-high confidence that it was behind the watering hole campaign.
How did the attack work?
The attackers hijacked the Ukrainian analytics service Plerdy and injected JavaScript into its tracking script. The script profiled visitors' browsers and devices, then served platform-specific n-day exploit chains without user interaction.
What data was stolen?
Depending on the device, the exploits stole cookies, messaging app databases (WhatsApp, Telegram), Keychain credentials, location data, photos, Chrome cookies, login data, browsing history, and Wi-Fi passwords.