Microsoft ties China-linked Storm-0940 hackers to ConnectWise attack on 2,250 tenants
Microsoft Threat Intelligence tied China state-aligned group Storm-0940 to an AI-driven campaign abusing a ConnectWise supply chain compromise, hitting more than 2,250 tenants with 2,900 sign-in attempts per minute.
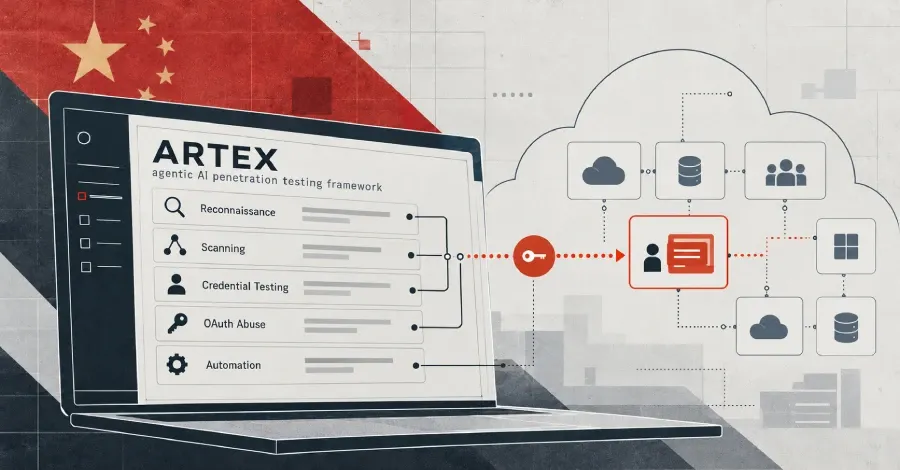 Photo: The Hacker News
Key points
Microsoft linked China state-aligned group Storm-0940 to a ConnectWise supply chain attack using the ARTEX AI framework, affecting more than 2,250 tenants.
Microsoft linked a China state-aligned hacking group it tracks as Storm-0940 to an attack on IT services firm ConnectWise, part of a campaign that targeted hundreds of organizations globally. The group used an AI-driven penetration-testing tool called ARTEX to carry out the campaign, Microsoft said on Wednesday, in a report released 21 October 2026.
The attribution matters because it ties a specific named group to a supply-chain compromise that opened doors at many downstream customers at once. Unlike a single-target break-in, the ConnectWise breach let attackers move through shared cloud infrastructure to reach privileged access at many organisations, in some cases within three hours of the first foothold.
What Microsoft's report says
Microsoft's report, released 21 October 2026, ties Storm-0940 to a sprawling campaign run through ARTEX, an AI-driven penetration-testing framework. In some incidents, the group moved from a first foothold to elevated cloud privileges in less than three hours. Microsoft said Storm-0940 achieved privileged cloud persistence — high-level access that could continue even after cleanup efforts — at many organisations in a brief time.
ConnectWise CEO Manny Rivelo said it appeared a China state-aligned group was responsible for the attack on ConnectWise Cloud Backup, based on Microsoft's analysis and evidence available to ConnectWise. Rivelo said the company contained the affected application connections and is restoring services in controlled phases, but those actions do not remove unauthorised access that may already exist within individual customer tenants.
ARTEX automates penetration testing — legitimate testing of a network's or service's security — using AI. Microsoft said ARTEX lets users plug in any AI model to automate tasks and can run autonomous operations, including reconnaissance and data exfiltration. Storm-0940 used it to run several attack phases on autopilot, including reconnaissance and exploitation, across hundreds of organisations.
Where the numbers came from
The attack targeted organizations across aerospace, defence, automotive, chemicals, energy, financial services, government, legal, manufacturing, media, military, semiconductor, software, technology, think tanks and non-profit organisations, Microsoft said. ARTEX was released in July 2026 for legitimate security testing, then went closed-source in October 2026 following reported misuse; before the ConnectWise attack it was linked to breaches affecting roughly 68,000 individuals at South Korean financial institutions.
A spokesperson for the Chinese Embassy in Washington said China opposes and fights hacking activities in accordance with the law, and opposes smears and attacks against China under the excuse of cybersecurity issues. Microsoft's research places Storm-0940's activity back to at least 2021, making the group no newcomer to this kind of campaign.
What happens next
Microsoft's practical guidance focuses on service principal sign-ins — non-human accounts that often hold broad permissions. Security teams are advised to audit which third-party apps hold OAuth permissions, monitor service principal activity for unusual volume, and treat sudden bursts of authentication attempts, such as 2,900 per minute, as an alarm.
Frequently asked questions
Who did Microsoft link to the ConnectWise attack?
Microsoft Threat Intelligence tied the threat actor it tracks as Storm-0940, described as a China state-aligned group, to the attack on ConnectWise and the wider campaign using the ARTEX framework.
What is the ARTEX framework?
ARTEX is an AI-driven penetration-testing framework that automates security testing tasks. Released in July 2026, it went closed-source in October 2026 after reported misuse, and can run autonomous reconnaissance and data exfiltration.